Staying Frosty: How to Keep Calm and Stay Alert Against Spoofing and Phishing

Staying Frosty: How to Keep Calm and Stay Alert Against Spoofing and Phishing

By Micah Ulrick, vCIO

IN THIS ARTICLE: 

We’ve said it before, but I’ll say it again, cybersecurity is more critical than ever. As a vCIO, I advise my clients on cybersecurity daily. While ransomware, DoS (Denial of Service), and Brute Force attacks are still a thing, phishing and spoofing are still two of the most common and dangerous threats today. These are the primary causes of compromises.

The problem is there’s no magic bullet that will 100% protect you from these attacks. So, understanding these threats and how to identify them can make all the difference in protecting both you and your organization from significant harm.

Every time you venture into your inbox or out onto the web, remember these tips to stay frosty (a.k.a. cool and alert) against the dangers of phishing and spoofing.

Understanding Spoofing & Phishing: What You Need to Know

Spoofing is when a threat actor masquerades as a trustworthy company or contact by faking their email, caller ID number, or website. Spoofing is effective because it manipulates your confidence in well-known companies or acquaintances and relies on the human habit of quickly scanning messages and missing signs that it’s a fake.

Spoofing is typically used in phishing, a technique used by cybercriminals to trick you into willingly handing over sensitive information, such as passwords, credit card and banking information, or personal and corporate data. These attacks often come in the form of emails or texts that appear to be from legitimate sources, such as banks, vendors, or even colleagues.

In simple terms: spoofing is the faking of “who” you’re talking to, and phishing is “how” they engage with you to take action. Like actual ‘fishing’, they’re trying to hook you with deceptive bait so they can reel you in.

How to Spot Spoofing and Phishing Red Flags

Identifying Spoofs

Email Spoofing

Signs of Spoof: Inconsistencies like slight misspellings in email addresses, domain names, and display names, or emails that come from a different domain name than usual.

  • Always scrutinize email addresses, domain names, and display names.
  • Talk to your IT provider about adding an “external” banner to flag emails coming from outside your organization to enhance awareness.

Caller ID and Text Spoofing

Signs of Spoof: Unexpected calls or texts from both familiar and unfamiliar numbers claiming to be someone you know. Scammers can manipulate caller ID information to make calls or texts appear as though they are coming from a trusted contact or organization.  

  • Look out for links in text messages (don’t click them) 
  • Be wary of abnormal requests. 
  • If you receive an unexpected call or text from a colleague, stop engaging and re-initiate contact in person or using a verified number or communication source you can trust.

Website Spoofing

Signs of Spoof: Spoofed websites may look identical to legitimate ones but have different URLs. They may also be missing “HTTPS” in the URL. The security padlock symbol in the address bar of the browser may also be missing.

  • Always double-check the URL spelling.
  • Check the name for familiarity. For example, “https://your-company.com” versus “https://yourcompany.com”.
  • Look for HTTPS and the padlock symbol in the address bar. If these are missing it’s not a good sign.

Avoid Falling for Phishing

  • Scrutinize Sender Addresses: Always check the sender’s email address. Phishing emails are often spoofed and come from legitimate-sounding addresses. Look for those slight alterations in the domain name, display name, and sender address. For instance, an email from “support@closolutions.com” instead of “support@ciosolutions.com”. Did you catch the difference at first glance? That’s how subtle they are. Look closely!
  • Beware Generic Greetings: Be cautious of emails with generic greetings like “Dear Customer” instead of your name. This is usually an indication that it’s a mass email blasted to many recipients and is a warning sign that something’s not right.
  • Resist Being Rushed: Look out for “account closure” notices, “unauthorized transaction” warnings, “password update needed”, or phrases like “Your account will be locked in 24 hours” or “Immediate action required”. Phishing emails often try to rush you into a mistake by creating a sense of urgency. Take a breath, and if you’re concerned, log into the questionable account as usual (not from any links in the email) to make sure everything is as it should be.
  • Note Unusual Requests: If an email is requesting information such as passwords, social security numbers, or credit card details via email, especially out of the blue, it’s likely a phishing attempt. Remember that legitimate organizations will never ask for sensitive information like this via email. Put your antennae up for these and note the strangeness of the request.
  • Don’t Click That Link or Attachment: Hover your cursor over the link text to see the actual embedded URL destination before clicking. Opening your email on a phone? Avoid the risk altogether and go directly to the website instead of clicking on a link. Phishing links often present themselves as one thing but really lead to malicious URLs. Similarly, be wary of attachments, especially if you weren’t expecting them. When in doubt: Don’t. Click.

Advanced Threats to Be Aware Of

Now that we’ve covered the basics of phishing and spoofing, there are several advanced threats that pose significant risks. Understanding these can further enhance your cybersecurity posture.

Whale-Phishing Attacks: Watch Out, C-Suite

Whale-phishing, or whaling, targets high-profile C-Suite individuals such as CEOs or CFOs. These attacks are highly personalized and sophisticated, aiming to steal sensitive corporate information or execute fraudulent transactions. Due to the high stakes involved, whaling emails often appear very legitimate and may reference actual company projects or executives by name, or ask for a change in payroll accounts. Bad actors typically gather this data by compromising lower-level employees with the phishing and spoofing tactics above.

Spear-Phishing Attacks: We Know You. No Really.

Unlike regular phishing, which is sent to a broad audience, spear-phishing emails are targeted and customized to the recipient, making them harder to detect. Bad actors often use information gathered from social media (LinkedIn, Facebook, etc.) and other online sources to spoof effectively and build convincing requests. These typically flow from the top down. For example, a threat actor may gather information about a CEO and will impersonate them to request a wire transfer from someone on the Finance team at their company.

Man-in-the-Middle (MITM) Attacks: You’ve Got Company

In an MITM attack, a cybercriminal first gains access so they can then intercept communication between two parties, for example between an Accounts Receivable rep at one company and an Accounts Payable rep at another. Once the attacker has access, they then “lie in wait” and eavesdrop to steal data or interject themselves into the communication chain to ask for a change in bank routing and account information or payroll information to steal money.

This is often done by compromising someone’s email, but unsecured Wi-Fi networks are also a common culprit, letting an attacker intercept data transmitted between your device and the network.

Remember These Best Practices

  • Be Skeptical: Always question unsolicited emails and calls. If something seems off, it probably is.
  • Slow Down: Don’t rush to respond, and don’t impulsively click on unknown links or attachments.
  • Keep Learning (and pass it on): Cybercriminals constantly evolve their strategies, so staying up-to-date and informed is crucial. Share this information with colleagues and loved ones to create a network of aware and cautious individuals.
  • Enable Multi-Factor Authentication (MFA): MFA adds an extra layer of security, making it harder for attackers to gain access to your accounts. This typically involves a second form of verification in addition to your password, such as a code sent to your phone or an authenticator application. Enable this whenever possible!
  • Keep Software Updated: Regular updates patch fixes for identified security vulnerabilities, making it harder for cybercriminals to exploit your system. This includes operating systems, browsers, and any other software applications you use (even your phone and apps).
  • Report Suspicious Activity: If you receive a suspicious email or call or think you may have clicked on a sketchy link, report it to your IT department or service provider. Prompt reporting can prevent widespread damage and help authorities track and stop cybercriminals.

It’s up to everyone to stay informed and vigilant. The most important things you can take with you when you venture online every day are patience and suspicion. Don’t be trigger-happy with your clicks and responses, and take the time to look at emails, texts, and websites a bit closer. Trust little and verify when possible.

Stay safe, stay aware, and stay frosty out there.


An Additional Note For Business Leaders:

With compromises on the rise, Cyber Liability Insurance has become an essential part of protecting your business in the event of an attack. All companies, big and small, can benefit from Cyber Liability Insurance and we highly recommend acquiring it.


Did you know that CIO Solutions offers automated phishing awareness training and simulated user phishing campaigns? Reach out to your vCIO or Customer Success Manager to learn more about including Knowbe4 in your monthly service agreement at no additional cost!

Not a client yet? Contact us today to talk through your options for enhancing your IT management and security.
Employee Spotlight: Adam J. Fernandes

Employee Spotlight: Adam J. Fernandes
Behind the Screens- Meet Adam Fernandes
Meet Adam, a versatile member of the CIO Solutions team! For the past 2 years, Adam has used his wealth of expertise to ensure smooth hardware deployments for our clients. As a Deployment Technician, he visits our clients’ offices and interacts with people at all levels of the organization to assist with any issues or questions they may face during these deployments. Adam’s commitment to helping our clients means he is always ready to go the extra mile to make a positive impact on their businesses and set them up for success.

Born and raised in San Luis Obispo, Adam holds an Associate’s degree in ‘Information Technology and Network Systems’ from Laurus College, and he landed his first IT job while still in school.

His creative passions extend well beyond the technical realm. Adam is also a screenwriter with over 70 screenplays to his name. He also worked as a chef for 15 years, plays guitar, and is an avid photographer (or as he puts it, “takes way too many photos”).

Read on to learn more about Adam!


What has been your proudest moment at CIO?

Professionally, being asked to be on the DOT (Deployments Team) on my first week.

Company-wise, winning both prizes in my first CIOBrew-Off with Tech-Tonic.


If you could go back to any moment in time, when would it be?

Prohibition-era New York. Sights, sounds, smells, and speakeasies.


Would you rather be the funniest or smartest person in the room? Why?

Funniest, because laughter brings people together.


What’s the weirdest fact you know?

The ‘Pizza Planet’ truck from Toy Story has appeared in every single Pixar film.


What’s your favorite famous or inspirational quote?

‘All men dream: but not equally. Those who dream by night in the dusty recesses of their minds wake up in the day to find it was vanity, but the dreamers of the day are dangerous men, for they may act their dreams with open eyes, to make it possible.’ – Thomas Edward Lawrence, aka ‘Lawrence of Arabia’


If you could learn to do anything, what would it be?

Fly a plane.


What’s something you’re planning on doing in the next year that you’ve never done?

Hopefully, visiting a country or a place I’ve never been to before.


What do you pretend to hate but actually love?

I don’t ‘pretend’ to hate things, but there are several rom-coms I love that might be surprising.


What could you give a 30-minute presentation on without any advance preparation?

Screenwriting.


If your life were a movie, who would play you?

John Cusack, my doppelganger.


—————————————————————————————————————————————————————-

Bonus: What 3 words would you use to describe CIO Solutions?

Empowering, Camaraderie, Hilarious


We are proud of our team of skilled and friendly individuals. It’s a unique group of collaborators and innovators who share a common “can-do” mentality paired with a fondness for gifs and puns. 

Looking for opportunities to join our team? Visit our Meet the Team page to see all open positions in our Santa Barbara, San Luis Obispo, and Fresno offices!


Email Authentication Protocols to Protect Your Business

Email Authentication Protocols to Protect Your Business

By Peter Summers, vCIO

IN THIS ARTICLE: 

Email is an essential tool for businesses and individuals alike, making it a prime target for cybercriminals. Protecting your business against email-based attacks goes beyond having the latest threat detection tools and educating your users not to click on suspicious links.

Here are a few more technical email security measures, including DKIM, DMARC, and SPF, that organizations need to implement to cover their foundational bases.

Email Authentication Protocols: DKIM, DMARC, and SPF

DKIM, or DomainKeys Identified Mail

This is a protocol that enables email recipients to verify that an email is really from the sender it says it’s from and that it hasn’t been tampered with or modified during transit. DKIM works by adding a digital signature to the header of an email message when it’s sent. That signature is then verified by your email provider using a public key published in the DNS (Domain Name Server) records for the domain. If it’s checked and found to be a valid signature, the email is in fact from the sender it claims to be from and hasn’t been tampered with.

SPF, or Sender Policy Framework

SPF is an email authentication protocol that enables domain owners to specify which IP addresses are authorized to send emails on their behalf.

For this protocol, the domain owner publishes a list of authorized IP addresses in the DNS records for the domain. Email providers can use this information to confirm that emails claiming to be sent from this domain are truly coming from the approved list of IP addresses.

DMARC, or Domain-Based Message Authentication, Reporting, and Conformance

This protocol builds on DKIM and SPF by providing a way for domain owners to declare their email authentication policies and receive reports on how their emails are being handled by email providers. Giving domain owners this ability to keep an eye on their email traffic and detect unauthorized use of their domains can be incredibly useful for helping to prevent phishing and other kinds of email-based attacks.

A Dynamic Trio

DKIM, DMARC, and SPF work together behind the scenes to provide a more powerful defense against email-based attacks. Increasing the ability of email recipients to verify the authenticity of incoming email messages alone is a huge security improvement. Pair that with the ability for domain owners to specify the use of their domain name, monitor their email traffic, and detect and block unauthorized use of their domain name, and these protocols can help prevent phishing, spoofing, and other types of email fraud.

These protocols are more on the complex technical side, and they require careful planning and configuration. Be sure to work with experienced email security experts to set them up correctly and get your organization more protected against email-based security threats.


Already a client of CIO Solutions? Reach out to your vCIO to discuss DKIM, DMARC, and SPF and where it fits in your email security plan!

Not a client yet, but curious about learning how to boost your organization’s security posture? Let’s talk about your options!

Employee Spotlight: Fernando Rivera

Employee Spotlight: Fernando RiveraBehind the Screens- Meet Fernando Rivera
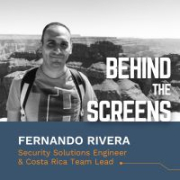
Let’s introduce you to Fernando Rivera, who has been an integral part of the team at CIO Solutions for 16 years. Fernando works out of our Costa Rica office, where he leads a team of talented and dedicated IT professionals while also performing his duties as a security solutions engineer.

Fernando lives between two of the nicest provinces in Costa Rica, Alajuela and Heredia, where he spends time with his girlfriend and his dog and enjoying the coolest sunsets. He is a fan of TV shows and series, playing video games, and taking care of his fish tanks (a self-proclaimed obsession). He started with a small tank (10 gallons) and has since moved up to a whopping 100-gallon one! Fernando’s love of nature doesn’t stop at his fish tank- he’s a nature fanatic and loves animal photography. It’s an advantage that his girlfriend owns a travel agency! He invites all to visit Costa Rica and experience the beautiful nature and diverse animals.

In his role as a security solutions engineer and Costa Rica team lead, Fernando has a lot of responsibilities. He and his team help protect our clients’ data and systems from cyber threats through cybersecurity solutions, patch management, and antivirus solutions. As a team lead, he guides, instructs, and directs his team in delivering the highest-quality service possible. Fernando recognizes the fundamental importance of embracing growth and keeping an eye on the changes in the technological world to keep our clients safe and happy. Over the years, he has earned several certifications and credentials, such as CompTIA A+, Network +, CrowdStrike Falcon Platform Technical Fundamentals, Sophos Certified Engineer, Webroot Endpoint Technical Certification, Windows 10 Technical Fundamentals, Watchguard Firmware Essential Certification, and Web Designer University.

Read on to learn more about Fernando!


What has been your proudest moment at CIO?

When I had the opportunity to visit and meet my coworkers in San Luis Obispo.


How would your family or friends describe you in three words?

Smart, trustworthy, and helpful


Who is your hero? Why?

I don’t have one hero. I have heroes: My family


What’s the best advice you’ve ever heard?

Whatever you can do, give your 100%


If you could go back to any moment in time, when would it be?

College, because at my college we got the opportunity to work in a company to get a better understanding of what life really looks like for someone in that job. I got all my best knowledge during college.


If you could learn to do anything, what would it be?

Digital animation for movie projects


If you could have an unlimited supply of one thing, what would it be?

Water, I think is the most valuable natural thing we have and we need it in everything


What’s something you’re planning on doing in the next year that you’ve never done?

I am planning to visit one of the seven wonders of the world (Machupichu – Perú)


If you could have any superpower, what would it be?

Eldritch Magic used by Masters of the Mystical Arts (Dr. Stephen Vincent Strange – Marvel Comics)


What could you give a 30-minute presentation on without any advance preparation?

How to maintain a fish tank with good conditions


—————————————————————————————————————————————————————-

Bonus: What 3 words would you use to describe CIO Solutions?

Leadership, Innovative, Competitive


We are proud of our team of skilled and friendly individuals. It’s a unique group of collaborators and innovators who share a common “can-do” mentality paired with a fondness for gifs and puns. 

Looking for opportunities to join our team? Visit our Careers page to see all open positions in our Santa Barbara, San Luis Obispo, and Fresno offices!


[vc_row][vc_column][vc_btn title=”Contact Us” style=”custom” custom_background=”#fa8c19″ custom_text=”#ffffff” shape=”square” size=”lg” align=”center” link=”url:https%3A%2F%2Fwww.ciosolutions.com%2Fcontact%2F|title:Contact”][/vc_column][/vc_row]

Employee Spotlight: Billy Godfrey

Employee Spotlight: Billy GodfreyBehind the Screens- Meet Billy Godfrey
Billy Godfrey is a long-time member of CIO Solutions, celebrating 10 years with us as of this month! He is the supervisor of one of the Support Department’s Dedicated Client Teams (team Helios, to be exact). These Dedicated Client Teams are just that- dedicated to a specific set of clients so they develop a deep understanding of their unique environments, needs, and preferences when a complex support issue comes up and needs a deeper dive. As Billy says, “making the client happy is what it’s all about!” 

Billy has a fascinating personal story. He was born in Oklahoma and moved to Ocean City, New Jersey, then Virginia Beach, Virginia, where he graduated from James Madison University. He then moved to Santa Barbara, California, where he lived for about eight years. He met his wife way back in seventh grade, and they were married in the Bahamas, celebrating with about 80 of their guests on a beautiful island called Elbow Cay. They now have three children: two boys, ages four and two, and a girl who just turned six months.

Two years ago, Billy and his family moved to Naples, Florida, where they have a little over an acre of land for their kids to run wild. He loves spending time with people. In the past, that meant hanging out with friends, but now it’s all about family and watching his kids grow up. 

Read on to learn more about Billy!


What would the title of your autobiography be?

If you are not having fun, it is not worth it


What has been your proudest moment at CIO?

Winning HDI Southern California Support Technician of the Year Award


What’s something most people don’t know about you?

I have driven cross-country 17 times and LOVE IT!


How would your family or friends describe you in three words?

Fun, easygoing, and full of energy


What’s the best advice you’ve ever heard?

“When life gets you down, you know what you gotta do? Just keep swimming.” – Dory


What was the most unusual or interesting job you’ve had?

Working at a gas station when I was 12 years old. Get paid under the table to pretty much stock the cold drinks and make coffee. I would also get to take home any non-sold Krispy Kreme donuts at the end of the day.


If you could go back to any moment in time, when would it be?

My wedding week in the Bahamas.


Would you rather be the funniest or smartest person in the room? Why?

Funniest – fun people have more fun.


What’s your favorite famous or inspirational quote?

If you are not having fun, it is not worth it – Billy Godfrey (this was also my Senior year quote in High School)


If you could learn to do anything, what would it be?

Be creative. This is why I married my wife – opposites attract.


What’s something you’re planning on doing in the next year that you’ve never done?

Maybe getting chickens


What do you pretend to hate but actually love?

Drama shows – like reality TV


What’s your favorite TV show? Why?

Seinfeld – there is a little bit of everything in that show!


What’s the weirdest food you’ve ever eaten? How was it?

I am a pretty picky eater so not sure I have even tried anything weird.


If you could have any superpower, what would it be?

I think flying but really any would be cool.


What could you give a 30-minute presentation on without any advance preparation?

Almost anything – I like talking even if I don’t know what I am talking about.


If your life were a movie, who would play you?

Jim Carrey


—————————————————————————————————————————————————————-

Bonus: What 3 words would you use to describe CIO Solutions?

Fun, exciting, family-like


We are proud of our team of skilled and friendly individuals. It’s a unique group of collaborators and innovators who share a common “can-do” mentality paired with a fondness for gifs and puns. 

Looking for opportunities to join our team? Visit our Careers page to see all open positions in our Santa Barbara, San Luis Obispo, and Fresno offices!


[vc_row][vc_column][vc_btn title=”Contact Us” style=”custom” custom_background=”#fa8c19″ custom_text=”#ffffff” shape=”square” size=”lg” align=”center” link=”url:https%3A%2F%2Fwww.ciosolutions.com%2Fcontact%2F|title:Contact”][/vc_column][/vc_row]

Fast and Furious: Here Comes The ‘New Teams’

Fast and Furious: Here Comes The ‘New Teams’

By Josh Farlow, Director of Cloud Services

IN THIS ARTICLE: 

You have probably seen the Microsoft banners and pop-ups talking about ‘New Teams’ a lot lately. So much so, that it has become something we click past and forget about. But did you know that Microsoft has set a deadline to switch all users over to the New Teams? And that date is coming up quickly.  

Starting in July, the Classic version of Teams will not be an option any longer. In this article, we’ll talk about some of the technical reasons for this shift, the new features of New Teams, and on a business level, what this mandatory change means for your planning (both immediate and in the future). 

A Foundational Shift for Better Performance 

Who doesn’t want better performance? That is really the name of the game with New Teams. The Classic version of Teams was based on Electron and was much harder to maintain, update, and develop because of the custom nature of the product. This also meant the performance was lackluster, with no roadmap to improve further. The only option was for Microsoft to scrap it entirely and start from scratch. 

Enter WebView2.  

Microsoft Edge WebView2 is a control platform that allows developers to embed web technologies such as HTML, CSS, and JavaScript in their native applications. It uses the Microsoft Edge browser as its rendering engine to display web content in applications. This means developers can write code for a website or web app, and then reuse that web code in their Windows application, saving time and effort. Sounds awesome, right?  

What all this means is New Teams will run faster, use fewer resources, and can be updated rapidly so new features and security patches can be applied sooner. New Teams is just the start; Microsoft is rolling out this platform across all apps. We will talk about that in the future, but the short story is that as this is rolled out, both the native apps (the one you open on a desktop) and the web apps will look the same and have the same features.  

Security Developments in This New Model 

Since New Teams is built on an entirely new platform, that allowed Microsoft to rethink the strength of security within the code. Additionally, the deployment method used for New Teams is MSIX. This allows admins to push this out via Intune, as well as deploy it in a standard Windows Environment. When apps are deployed using MSIX, the location of the app install is invisible to the user, which ultimately provides better protection against attacks that would try to alter the installation. 

New Compatibility Requirements that Change the Legacy Game 

With the move to WebView2, the standardization across platforms (Web, Windows Native, MacOS, Citrix) will finally give us feature parity across platforms, not mixed experiences between each one.  

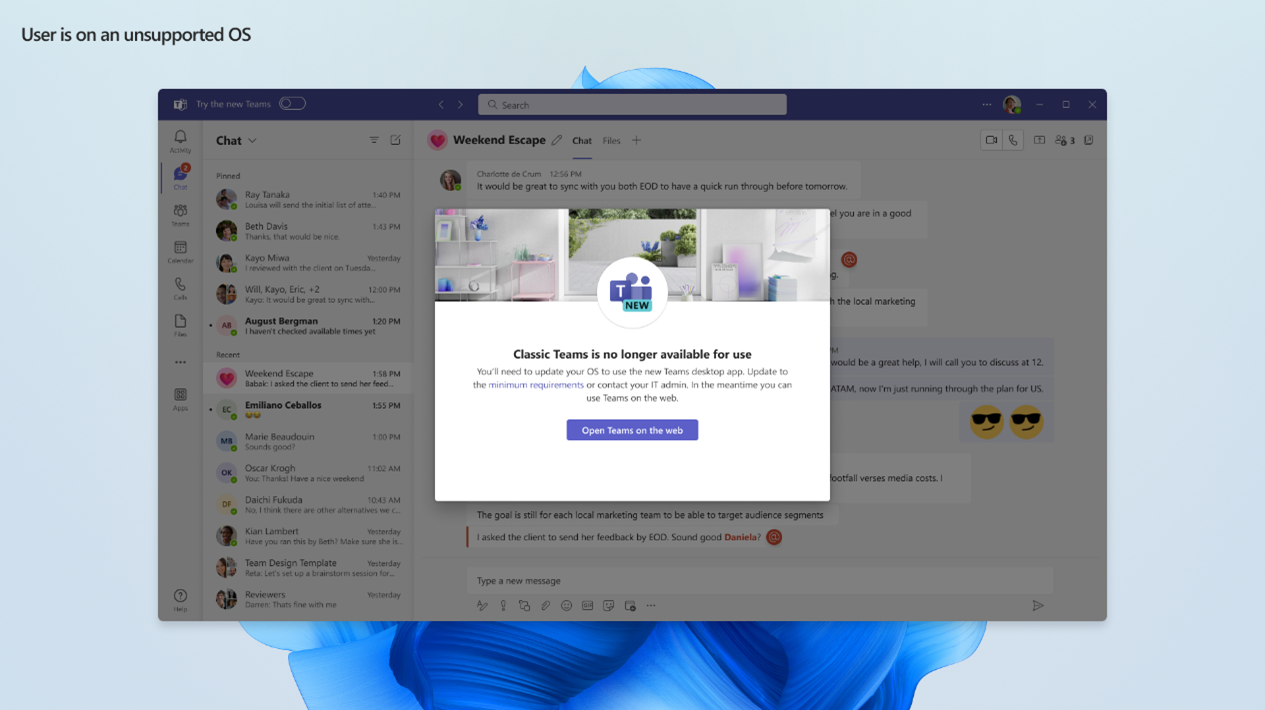
This is where Microsoft is drawing the line: the New Teams will NOT be supported on Server 2016 or Windows 10 LTSC or older.  

What this means: users who are running these versions (or older) will not be able to use the New Teams app. This could be a huge headache, especially considering how many businesses rely on Teams. 

However, there are a few directions to go. 

Immediate Solution: Run New Teams on the Web 

This may sound clunky, but if you recall from above, all platforms are the same experience with New Teams. The Web version is the same as the app version.  

Once the deadline hits, Classic Teams will not open or function. Users will be automatically redirected to use the Web version, so they will simply run New Teams from their browser instead. This is the message users will receive:

Fast and Furious: Here Comes The ‘New Teams’

Long-Term Solutions: Consider This in Your Planning 

As you can see, Microsoft’s move to New Teams is more than a refresh of a product, a game changer in architecture, design, and performance for not only this app, but the whole ecosystem moving forward. These changes will continue to create a ripple effect for customers, especially ones on an older operating system. 

If you’ve been considering a server upgrade, or are thinking about what’s next for your cloud environment, here are some options to consider:  

Upgrade to Server OS 2022 

What better time to upgrade than now? Whether you’re running your own servers on-premises or using a private cloud solution (like the CIO Private Cloud*), if your infrastructure relies on Server 2016 or older, a server upgrade may be the best next move for you.  

*Despite Server 2022 having been around for a couple of years, it has finally reached the stage of maturity to now make it a viable standard platform for our CIO Private Cloud Desktop. Please reach out to your vCIO to discuss your current server year and explore server upgrade options.

Evaluate the Next Wave of Cloud Solutions 

  • VDI (Virtual Desktop Infrastructure) is a cloud desktop model recently made available within the managed services space. This infrastructure design is a shift from the classic Server Operating System model to a per-user Windows 11 Desktop Operating System one.​ It offers many productivity and performance benefits beyond just being compatible with New Teams. A solution like this could solve some of your business’s current challenges and pave the way for future advancements.

Interested in learning more about VDI? Reach out to your vCIO for a demo. It’s very impressive and I highly recommend taking a look!

  • Modern Office – Serverless architecture is a newer model of cloud computing that relies on Software as a Service (SaaS) solutions (primarily Microsoft 365), and the individual user’s workstation. This model would offer a great path forward as Microsoft continues to roll out this new architecture for the M365 suite, however, it requires careful consideration. This model is only a fit for specific business cases, so be sure to talk with your IT provider in depth before making a switch! 

Check out our on-demand webinar about CIO’s next-generation Cloud Desktop (VDI) and Modern Office [here]!  

Embracing the New Teams 

I hope this helps shed some light on what these seemingly random pop-ups and banners are about the “New Teams”. Now you know, this is more than just a new look, it really is a whole new Teams, especially under the hood.  

Knowing more about this now, it may seem like a big inconvenience is on the horizon. In some ways that’s true, but luckily there are options, both temporary and in the long run, to prepare your business to continue to adapt with the always-changing world of productivity solutions.  


Are you a current client of CIO Solutions? Please feel free to reach out with any questions or concerns! We look forward to helping everyone with this transition.

Not a client yet? Let’s explore your options!

A vCIO’s Perspective on MFA: Importance and Implementation

A vCIO’s Perspective on MFA: Importance and Implementation

By Joseph King, vCIO

IN THIS ARTICLE: 

I work with clients across every imaginable industry on a daily basis as a CIO Solutions vCIO. One thing that is true for every business, no matter the industry, is the need to safeguard sensitive information. Today, it’s foundational that every business uses multifactor authentication (MFA) on their critical platforms. But despite its undeniable importance, implementing MFA often faces resistance.  

Resistance to MFA Implementation: Acknowledging the Concerns 

Implementing MFA is not always met with open arms, and I understand that. Here are a few reasons some businesses hesitate to adopt this crucial security measure: 

  • Perceived Complexity: One of the main reasons businesses might resist implementing MFA is the fear that adding an additional layer of security might disrupt their operations or require extensive training for employees.
  • Employee Pushback: The prospect of incorporating extra steps into the authentication process may be met with apprehension, as individuals might find it inconvenient or time-consuming. If businesses have had challenges with employees adopting new technologies, this tends to be a concern.
  • Initial Setup Challenges: The fear of potential disruptions during the transition to MFA can create a reluctance to embrace it. 

The Pitfalls of Resistance: A vCIO’s Perspective 

While the concerns mentioned above are valid, they are only temporary discomforts. The risk of choosing not to adopt MFA on key business applications is much more significant than the potential nuisances during the transition. Let’s take a look. 

  • Incomplete Security Posture: Relying solely on passwords in an age of sophisticated cyber threats is like leaving a gate open to your business. MFA isn’t the end-all and be-all, but it’s one additional layer of prevention to a catastrophe.
  • Vulnerability to Phishing Attacks: Hackers love phishing attacks. MFA acts as a powerful shield against these attacks. Even if a user unknowingly falls victim to a phishing attempt and gives up their password to a threat actor, you still have that additional MFA defense in place that the bad guys don’t have.
  • Regulatory Compliance Concerns: Whether you’re trying to qualify for Cyber-liability insurance for your business (which you should be trying to do) or work in an industry that is subject to stringent regulatory standards, neglecting MFA puts you behind and at risk for a.) not qualifying for insurance or b.) being at risk for compliance consequences.  

How to Move Forward with MFA Implementation 

Multi-factor authentication is an investment in fortifying your digital defenses and ensuring the longevity of your business. Which applications are the most important for your business? Where do you store customer data? Financial information? Those should be priority number one. 

Advising a business on Multi-Factor Authentication (MFA) implementation requires a strategic approach to ensure a smooth transition while maximizing security benefits. Here are some key steps:

  1. Conduct a Security Assessment:
    • Conducting a comprehensive security assessment will identify existing vulnerabilities, potential risks, and areas where MFA can strengthen authentication processes. This assessment will provide valuable insights into the business’s current security posture and help prioritize MFA implementation efforts.
  2. Educate Stakeholders:
    • Key business stakeholders must be educated on the importance of MFA in enhancing security. The risks of relying solely on passwords and the benefits of adopting MFA, such as reducing the risk of unauthorized access and protecting sensitive data, need to be communicated and understood.
  3. Align with Business Objectives:
    • Aligning the MFA implementation strategy with the business’s broader business objectives and priorities is important. MFA supports and furthers many key initiatives, such as regulatory compliance, data protection, and maintaining customer trust, and highlighting this is useful for many stakeholders.
  4. Select the Right MFA Solution:
    • Selecting the MFA solution that best meets a business’s unique needs and requirements will ensure that the solution is a fit for successful adoption. It’s key to consider factors such as user experience, scalability, integration capabilities, and cost-effectiveness.
  5. Develop a Phased Implementation Plan:
    • Developing a phased implementation plan that outlines the steps involved in rolling out MFA across the organization makes the task of implementation much smoother. Start with a pilot program involving a small group of users or departments to test the MFA solution and gather feedback. Then, gradually expand the rollout to additional users and systems based on the lessons learned.
  6. Provide Training and Support:
    • Offering comprehensive training and support ensures a smooth transition to MFA. It’s key to provide clear instructions, step-by-step guides, and training sessions to educate users on how to set up and use MFA effectively.
  7. Monitor and Measure Effectiveness:
    • Implementing mechanisms to monitor the effectiveness of MFA implementation and measure its impact on security metrics will continuously boost the business’s security posture. Regularly reviewing and analyzing security logs and reports will allow for the identification of any anomalies or security threats.
  8. Stay Updated and Evolve:
    • The security world is constantly changing to adapt to threats. Staying informed about the latest developments in MFA technologies and best practices is crucial. A business’s MFA strategy should continuously be evaluated and updated to adapt to evolving security threats and changing business requirements.

In Conclusion

When a business decides to hold off on implementing MFA, that decision to avoid the temporary discomfort of adopting a new technology keeps them at an unnecessarily high degree of risk. Unfortunately, these days it’s not a question of “if” a business will experience a breach, it’s a question of “when”. Without this foundational tool in place, securing the business is significantly harder, and breaches are much more detrimental. 

All this to say, there are clear and tested paths forward to ensure that implementing MFA for your business is seamless and effective. I have seen this collection of steps work effectively for businesses of all sizes time and time again, and the risks of delaying by far outweigh the effort upfront of biting the MFA bullet.


Not sure where to start with MFA implementation? Don’t hesitate to reach out to your vCIO or Customer Success Manager!

Not a CIO Solutions client? Contact us to explore your options for securing and managing your IT!

Migrating from a File Server to OneDrive & SharePoint? Consider This

Migrating from a File Server to OneDrive & SharePoint? Consider This

By Josh Farlow, Director of Cloud Services

IN THIS ARTICLE: 

“Modern Office”: This may be a term you have heard, but it does not describe the updated finishes on your office building. Let’s talk about what Modern Office means and some of the important logistical considerations to keep in mind when it comes when making the leap to Modern Office solutions for File Management.

Modern Office refers to a business computing model defined by:

  1. Serverless Architecture – No more servers in your server closet or in a data center
  2. SaaS (Software as a Service) based applications – All apps are “in the Cloud”, and typically include Microsoft 365 in some form. In other words, they are software services paid on a subscription basis and hosted in a data center somewhere in the world.
  3. Modern File Management – File storage and management within OneDrive and SharePoint instead of a dedicated file server.

The appeal of embracing aspects of the Modern Office model, particularly the M365 (Microsoft 365) ecosystem and vision, is undeniable. It promises so many benefits: Intune for device management, Autopilot for ease of onboarding new users/computers, browser-based applications, and a combination of the performance of local resources with cloud flexibility.

Ditching the servers entirely and moving operations 100% toward a serverless Modern Office model is only feasible for certain businesses. But across the board, businesses are starting to incorporate one key piece of this Modern Office model into their operations: File Storage and Management via OneDrive and SharePoint in M365. However, there are many considerations and challenges to consider when making this transition.

The Power of OneDrive and SharePoint 

The OneDrive and SharePoint platforms are the foundations of cloud-based collaboration and storage within the M365 ecosystem. They empower users to seamlessly access, share, and collaborate on documents – the dream for a modern, interconnected workspace.

However, because they’re so foundational, before you jump in, it’s important to bear in mind that a thoughtful, strategic approach will help you not only maximize their effectiveness but also avoid potential pitfalls.

Strategic Considerations

It would be great if the transition was as simple as uploading your files and calling it a day. A few challenges keep things interesting.

Syncing Issues and File Corruption– File corruption is a common issue since the underlying technology of these cloud platforms is different from your traditional file servers.

  • Because they speak a different language, a direct transfer of the existing file server structure may lead to problems that interrupt user productivity. If many of your files are suddenly corrupted when users try to access them, they may find themselves spending the rest of the day on the phone with the support.
  • OneDrive software can simply stop working or syncing. This can be caused by a myriad of issues such as token expirations, local resource contention, file path limitations, number of files syncing limits, etc.
  • File folder sizes can cause issues if there are too many folders within folders.

Third-Party Application Integration– The nature of your data and how users synchronize it can play a pivotal role.

  • SharePoint in particular poses a unique challenge. A write-heavy application may demand synchronization with multiple users, increasing the odds of metadata synchronization issues or corruption.
  • Applications that need to write back to a file server would first need to be pointed to a SharePoint document library. However, the way the application talks to SharePoint can cause major performance issues that would need to be accounted for.

Strategies & Tools for a Smooth Transition 

If you’re thinking that moving to OneDrive and SharePoint sounded great at first, but now it seems like a nightmare. Fortunately, there are strategies and innovative tools to make it easier!

  • Reducing Complexity

Let’s talk strategy first. One of the simplest and most effective approaches is to create multiple SharePoint sites rather than one all-encompassing one for all the company’s data. Often this looks like department or team-specific SharePoint sites.

Approaching your data in these smaller segments of department or team data serves a dual purpose – it reduces the number of users connecting to their respective document libraries at any time, and it trims down the size of data and the number of files. By doing so, the likelihood of metadata synchronization issues is significantly decreased.

  • Tools for a Seamless Migration

Effective tools have emerged to simplify this migration process, like Cloud Drive Mapper by IAM Cloud, for instance. Rather than relying on a syncing tool (OneDrive client), Cloud Drive Mapper operates in the same way as a mapped network drive, such as your S: drive, in a traditional file system. Cloud Drive Mapper facilitates seamless mapping of drives to M365 to provide a real-time connection to the SharePoint document library, no syncing required, no metadata issues. 

Unlocking the Potential 

In the grand scheme of things, embracing the power of OneDrive and SharePoint for file management can be revolutionary for your business. However, as we’ve explored in this article, the journey requires a strategic mindset and a proactive approach to navigate and avoid potential challenges.

As our team has seen in the real world, thoughtful consideration, coupled with tools like Cloud Drive Mapper, can pave the way for a seamless transition and ensure businesses can unlock the full potential of these Modern Office solutions without the headache and loss of productivity that might occur by jumping in blindly.


Are you a current client of CIO Solutions? Talk to your vCIO to continue the conversation!

Not a client yet, but curious about maturing your productivity tools? Let’s talk!

CIO Solutions Recognized on CRN 2024 MSP 500 List

CIO Solutions Recognized on CRN® 2024 MSP 500 List

Santa Barbara, CA, February 13, 2024 — CIO Solutions, Productivity Enhanced, announced today that CRN®, a brand of The Channel Company, has named CIO Solutions to its Managed Service Provider (MSP) 500 list in the MSP Pioneer 250 category for 2024.

The MSP 500 list is compiled by CRN annually and serves as a comprehensive guide to identifying and recognizing the top Managed Service Providers (MSPs) in North America. The MSP 500 list aims to showcase and celebrate MSPs that are driving growth and innovation in the industry. These service providers not only enable businesses to harness complex technologies but also contribute to maintaining a strong focus on core business goals without stretching financial resources.

The MSP Pioneer 250 section of the annual MSP 500 list recognizes companies with business models weighted toward managed services and largely focused on the SMB market. By providing comprehensive managed strategy, infrastructure, and support services, MSPs like CIO Solutions offer small to medium businesses access to the resources and benefits of a robust IT department without the hassle and cost of building and managing it themselves. Access to these expert services is more important than ever in today’s technology-dependent business landscape. For those businesses, MSPs enhance efficiency, simplify technology management, mature IT solutions, and optimize return on IT investments.

CIO Solutions serves over 300 California businesses ranging in size from 10-500+ employees. Their services include a robust support system designed with a “first contact resolution” support model, strategic technology planning services, a dedicated network operations center, and extensive infrastructure project and management services. Over the past 10 years, they have expanded their geographical reach to better serve clients throughout Central California and beyond, with three locally serving offices and 100 employees overall.

They embrace a forward-thinking approach and offer solutions that are not only proven and tested, but innovative. Among CIO Solutions’ offerings are advanced cloud computing, next-generation managed security, and modern office solutions. They maintain global partnerships including Citrix, Microsoft, Datto, and CrowdStrike.

Jennifer Follett, VP of US Content and executive Editor CRN, The Channel Company, emphasized the significance of managed services for businesses at various scales, stating, “Managed services provide a route for businesses of all sizes to maintain efficiency and adaptability throughout their growth journey. The solution providers featured in our 2024 MSP 500 list are introducing cutting-edge managed services portfolios to the market, enabling their clients to achieve success by optimizing their IT budgets. This allows businesses to allocate resources strategically, concentrating on mission-critical tasks that drive future success.”

Eric Egolf, CEO of CIO Solutions, says “We are thrilled to be recognized as an MSP 500 recipient. It is a reflection of our focus on matching our service offerings with the constantly evolving landscape in the MSP space. It’s fun to remember how different that MSP space was just 6 years ago and how quickly it continues to evolve.”

The MSP 500 list will be featured in the February 2024 issue of CRN and online at www.crn.com/msp500.

About CIO Solutions

CIO Solutions, a leading IT solutions provider based in California, has been delivering expert IT services and exceptional customer service since its establishment in 1986. With offices in Santa Barbara, Fresno, and San Luis Obispo, CIO Solutions offers innovative solutions across a wide range of sectors to ensure clients can maximize their time and resources through effective technology. CIO Solutions continues to grow year after year, driven by their mission to enrich lives through technology. www.ciosolutions.com

About The Channel Company

The Channel Company enables breakthrough IT channel performance with our dominant media, engaging events, expert consulting and education, and innovative marketing services and platforms. As the channel catalyst, we connect and empower technology suppliers, solution providers and end users. Backed by more than 40 years of unequalled channel experience, we draw from our deep knowledge to envision innovative new solutions for ever-evolving challenges in the technology marketplace. www.thechannelco.com

Follow The Channel Company: Twitter, LinkedIn, and Facebook.

© 2024 The Channel Company LLC. CRN is a registered trademark of The Channel Company, LLC. All rights reserved.

The Channel Company Contact:

Employee Spotlight: Kevin Tran

Employee Spotlight: Kevin Tran

Meet Kevin, a seasoned Project Engineer out of our San Luis Obispo office with six years of dedicated service at CIO Solutions (time flies!).

Born on the island of Honolulu, Hawaii, at the age of 4 Kevin moved to Perris, California. He spent much of his life in the Inland Empire, then after college, he bounced around places as far as Niagara Falls, NY. Eventually, he settled in on the Central Coast to be back with his family. When he’s not working during the week or at one of the paintball fields in Central California on the weekends, he hangs out with his 2 little white fluffy dogs, adopted in 2022.

In his role as a Project Engineer, Kevin is responsible for building new servers and networks, along with managing that infrastructure through various projects. He and the rest of the project team do a little of everything, from patching urgent security vulnerabilities to migrating applications and email platforms. “There’s actually very little technical stuff I can think of that we don’t take on in this department.”

Armed with a trifecta of CompTIA certifications—A+, Network+, and Security+—Kevin’s expertise extends beyond the norm, boasting a deep understanding of Linux systems that he cultivated after spending a long time as a community contributor to various Linux distributions before embarking on his IT career.

He loves playing with embedded systems like off-the-shelf routers, NAS, or set-top-boxes and is proficient in C++, Ruby, and various shell-scripting languages. With a knack for diving into the intricacies of technology, Kevin is a true example of the blend of technical mastery and relentless curiosity that drives innovation!

Read on to learn more about Kevin!


What has been your proudest moment at CIO?

Probably winning tech-of-the-year and rookie-of-the-year in 2018. Talk about a surprise. Who knew interns could even be nominated for such things?


What’s the best advice you’ve ever heard?

“You have to dress for the job you want, not the job you have, and you have to start doing the work you want to be doing.” along with “Fake it ’til you make it” memes. I’ve found a lot of truth in similar advice over the years from my parents and mentors that you just have to: believe in yourself, persevere every day, and keep your eye on the goal.


What was the most unusual or interesting job you’ve had?

I managed a cell phone accessories kiosk in the mall to support myself through college. You learn a lot about persuasion, pitching, and haggling in that kind of job. I laugh at it now, because that’s not at all what I thought I’d be any good at.


Would you rather be the funniest or smartest person in the room? Why?

Funniest. I think people who can entertain and resonate with others’ sense of humor have an incredible gift. To gain favor through interaction is a lot of what leads to successful outcomes in whatever the case may be. Funny people have that going for them.


If you could have an unlimited supply of one thing, what would it be?

Paintballs. If you know me, you probably saw that one coming a mile away.


What’s something you’re planning on doing in the next year that you’ve never done?

Travel to Europe. Need to knock that off my bucket list. Everyone says it’s amazing.


What do you pretend to hate but actually love?

Cooking. Truth reveal: I pretend I don’t like it because I don’t want to cook for you, in case you don’t like it. But I actually do cook a lot and hardly go out to eat.


What’s the weirdest food you’ve ever eaten? How was it?

“Balut” it’s a Filipino delicacy. Google it. It’s like chicken broth in a shell if you eat it with your eyes closed.


If your life were a movie, who would play you?

For the lulz, Werner Herzog. I think it would be hilarious to see him play anyone in a biopic. Just look and listen to the man in any interaction.


—————————————————————————————————————————————————————-

Bonus: What 3 words would you use to describe CIO Solutions?

Excellence, Organized, Fun


We are proud of our team of skilled and friendly individuals. It’s a unique group of collaborators and innovators who share a common “can-do” mentality paired with a fondness for gifs and puns. 

Looking for opportunities to join our team? Visit our Careers page to see all open positions in our Santa Barbara, San Luis Obispo, and Fresno offices!


[vc_row][vc_column][vc_btn title=”Contact Us” style=”custom” custom_background=”#fa8c19″ custom_text=”#ffffff” shape=”square” size=”lg” align=”center” link=”url:https%3A%2F%2Fwww.ciosolutions.com%2Fcontact%2F|title:Contact”][/vc_column][/vc_row]